Quick Summary:
Every endpoint a SaaS team ships adds risk, and most attacks now arrive with a valid token. Seven steps keep that risk measurable: inventory, risk scoring, token checks, an authorization matrix, input and rate-limit tests, CI/CD gates and repair metrics. Simple formulas size each step, and AI tools speed up the work. LLM endpoints, agents and mobile clients join the same test plan.
Table of Contents:
- Introduction
- 3 Numbers Behind the API Risk in SaaS
- 7 Steps to API Security Testing for SaaS Teams
- 4 Ways AI Changes Security Testing
- Final Say
- FAQs
Every new endpoint is a new door. A SaaS company adds endpoints through webhooks, partner integrations and AI agents that connect multiple services.
Salt Security’s 1H 2026 research found 66% of organizations grew their API count by more than 50% in a year.
Just 24% keep a fully automated inventory.
That is why API security testing now belongs in the sprint.
It checks that each endpoint verifies the caller, limits the data and survives misuse.
For a growing team, the method matters more than the headcount.
Seven steps and six formulas take you from API discovery to security checks within the release pipeline.
ImpactQA evaluates access controls and tenant-level security.
3 Numbers Behind the API Risk in SaaS
API security has become a larger part of application security testing as SaaS environments expose more endpoints.
1. $4.99 Million
Source: IBM Cost of a Data Breach Report 2026
That is the global average cost of a breach, up 12%.
The United States average sits at $11.5 million.
For a SaaS business with enterprise customers, a single incident also lands in every renewal conversation.
2. 43 Days
Source: Verizon 2026 Data Breach Investigations Report
That is the median time to fully patch a known exploited vulnerability, up from 32 days a year earlier.
Vulnerability exploitation now opens 31% of breaches, up from 20%, and third parties feature in 48% of incidents.
Hence, speed of repair has become a metric worth tracking.
3. 99%
Source: Salt Security 1H 2026 report
That is the share of analyzed attack attempts that came from authenticated sources.
The requests came from authenticated sources, showing why valid credentials alone cannot establish authorization.
So the sharpest test question moves from “who are you?” to “what may you touch?”
7 Steps to API Security Testing for SaaS Teams
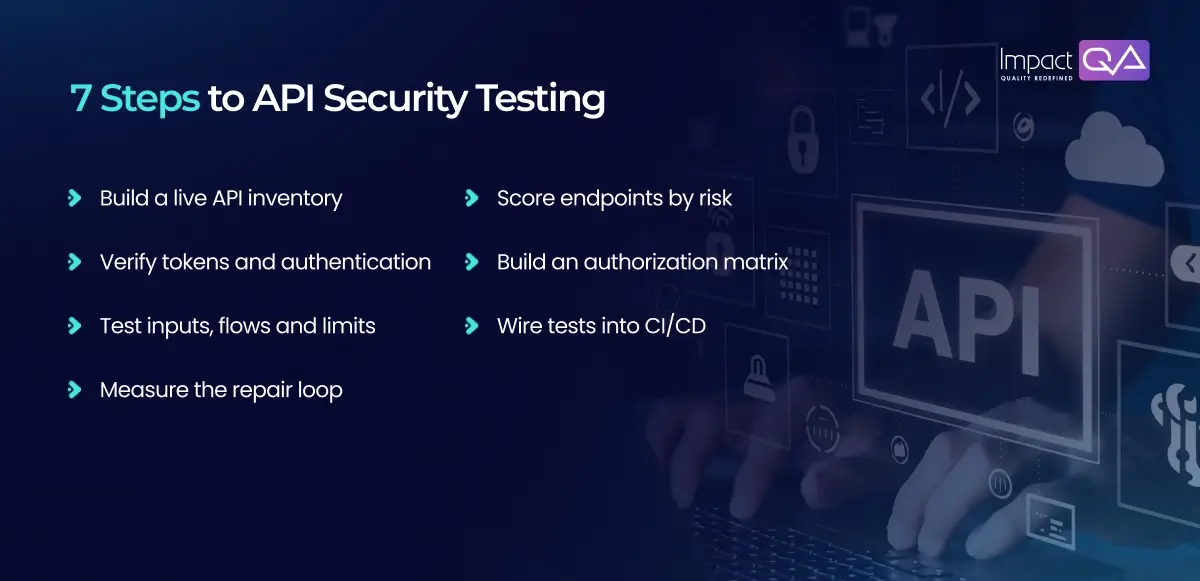
The sequence below maps to the OWASP API Security Top 10 (2023), still the working reference for API risk.
Each step feeds the next.
Step 1: Build a Live API Inventory
Maps to: API9, Improper Inventory Management
Start with your OpenAPI specifications, then compare them with gateway logs and traffic captures.
The gaps can reveal shadow APIs that lack documentation and zombie APIs left active after older versions were retired.
Record each endpoint’s owner, version, authentication type and data class.
Coverage % = (Endpoints Tested ÷ Endpoints Discovered) × 100
A team with 180 discovered endpoints and 135 under test sits at 75%.
Step 2: Score Each Endpoint by Risk
Maps to: Threat modeling
Testing time is finite, so spend it where a failure hurts most.
Rate three factors from 1 to 5, then multiply.
Risk Score = Exposure × Data Sensitivity × Business Impact
A public billing endpoint might score 5 × 5 × 5 = 125.
An internal health check might score 1 × 1 × 2 = 2.
Prioritize endpoints scoring above 60, and adjust the threshold to match your product’s risk profile.
Step 3: Verify Authentication and Tokens
Maps to: API2, Broken Authentication
Modify JSON Web Token (JWT) claims and verify that the server rejects tokens with invalid signatures or altered claims.
Validate the signature, expiration (exp), audience (aud) and issuer (iss) claims.
Send a JWT using the none algorithm and verify that the server rejects it.
Next, confirm that refresh tokens rotate after use and that OAuth scopes match the action.
For login routes, test lockout thresholds and credential stuffing limits.
Step 4: Build an Authorization Matrix
Maps to: API1, API3 and API5
This step carries the most weight in a multi-tenant product.
Broken Object Level Authorization (BOLA) tops the OWASP list for a reason.
Authenticate as Tenant A, request Tenant B’s record by ID and verify that access is denied.
Function-level checks access admin routes using a member token to verify role-based restrictions.
Property-level checks submit restricted fields, such as a role change, and verify that unauthorized updates are rejected.
Authorization Tests = Endpoints × HTTP Methods × Roles × Tenant Contexts
Twenty endpoints × 3 methods × 4 roles × 2 tenant contexts gives 480 checks.
That volume suits automation, so generate the matrix from your specification.
Step 5: Test Inputs, Flows and Limits
Maps to: API4, API6, API7 and API8
Fuzzing sends malformed payloads to identify parsing weaknesses; API schemas can help generate test cases.
Test URL-handling parameters for server-side request forgery (SSRF), where attackers manipulate server requests to reach internal resources.
For GraphQL, test query depth and introspection settings.
Rate limits deserve a measured test.
Exceed the configured rate limit and verify that the API returns HTTP 429, with a Retry-After header where supported.
Business flows need attention too, since a checkout or trial signup can be abused at machine speed.
Salt’s research names security misconfiguration in 65% of attacks, so review headers, CORS rules and verbose errors in every environment.
Step 6: Wire Tests Into the Pipeline
Maps to: DevSecOps
Static analysis (SAST) reads the code on every commit.
Dynamic application security testing (DAST) probes the running API in staging after deployment.
The authorization matrix runs nightly.
A specialist penetration test covers business logic on each major release, and our security testing services pricing guide explains how that depth shapes effort.
Set the gate plainly: a critical or high finding on a score above 60 holds the release.
Salt found 47% of organizations delayed production releases over API security concerns, so early tests protect the calendar too.
Step 7: Measure the Repair Loop
Maps to: Reporting and retest
Two numbers show whether the program works.
Mean Time to Remediate = Total Remediation Time ÷ Findings Closed
Escape Rate % = (Production Findings ÷ Total Findings) × 100
Twelve production findings out of 150 gives an 8% escape rate.
Review both monthly, and retest every fix before closing the ticket.
4 Ways AI Changes Security Testing
AI in security testing now runs in two directions.
It speeds up the tester, and it adds new surfaces to test.
1. AI Security Testing Tools
Use: Speed and coverage
AI security testing tools read a specification and draft negative cases, then cluster duplicate findings for faster triage.
Engineers still confirm each finding before it reaches a developer.
2. Agentic AI Security Testing
Use: Multi-step attack paths
An agent can log in, explore, change its plan and chain several requests, much as a human tester does.
Agentic AI security testing also runs in reverse, checking the agents you deploy for excessive privileges and unsafe tool use.
Scope these runs to a staging tenant with synthetic data.
3. AI & LLM Security Testing
Use: Model-backed endpoints
An LLM feature is an API with a probabilistic backend.
The OWASP Top 10 for LLM Applications 2026 keeps Prompt Injection at first place and lifts Excessive Agency to third.
So test whether a retrieved document can redirect the model, and whether the model’s tools respect the caller’s permissions.
Unbounded Consumption also rose to sixth, which makes cost a security metric.
Hourly Cost Exposure = Requests per Hour × Tokens per Request × Price per Token
Cap that figure at the gateway, then test the cap.
4. Mobile Application Security Testing
Use: Client-side API exposure
A mobile app ships its API calls to every device.
Mobile application security testing should confirm token storage, certificate validation and backend responses that return only the fields the screen needs.
ImpactQA combines security assessments and penetration testing to identify vulnerabilities.
Final Say
Gartner expects spending on securing AI to reach $4.8 billion in 2027, up 68.7%.
It also predicts that by 2029, over half of successful attacks on AI agents will exploit access control gaps and prompt injection.
Authorization testing will stay the center of the work, and teams that build these seven steps now will carry that discipline into every agent they ship.
ImpactQA’s security testing team of 50+ certified experts brings threat modeling, SAST, DAST and penetration testing across REST, SOAP and GraphQL, with AI and LLM assurance for agents.
Frequently Asked Questions (FAQs)
Share this post


Related Posts
Our Case Studies